

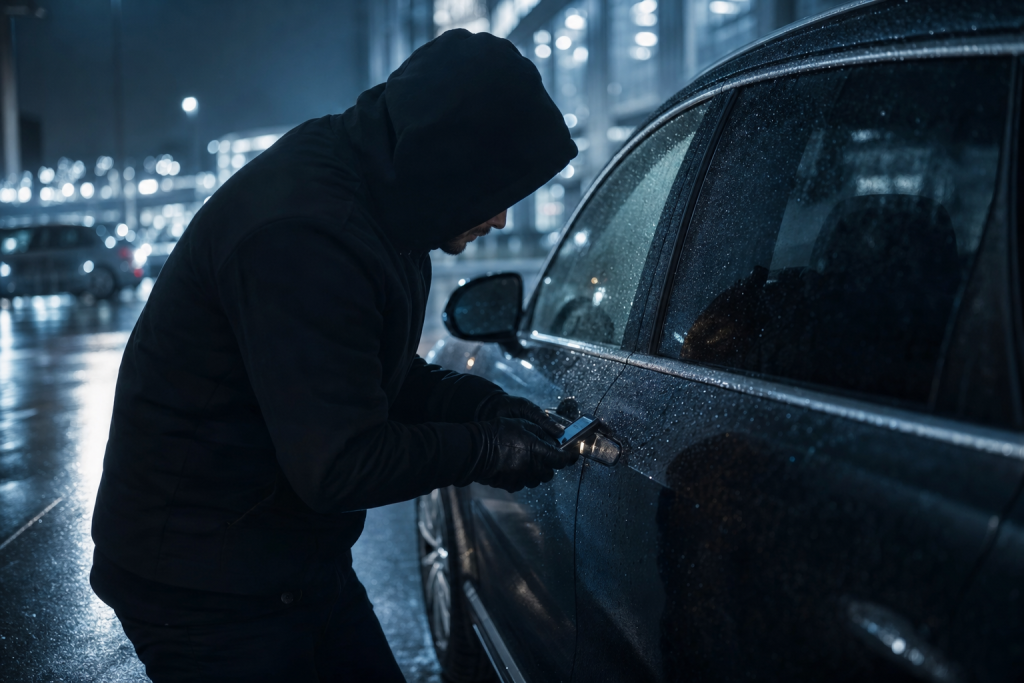
Two million cars with dealer-installed anti-theft systems are exposed via Bluetooth
Researchers at the University of California, San Diego, have discovered that at least 2.2 million cars with dealer-installed anti-theft systems are vulnerable to a Bluetooth attack. An attacker could lock or unlock the doors and even immobilize the engine remotely. The news is important because it highlights the risks of aftermarket systems and telematic integrations that do not receive the…
Read the article →
PR3TACK wants to map threats before attackers use them
PR3TACK is an open framework that seeks to bridge the gap between what attackers have already done and what they might do tomorrow. Instead of simply cataloging techniques observed in real incidents, the project…
Read the article →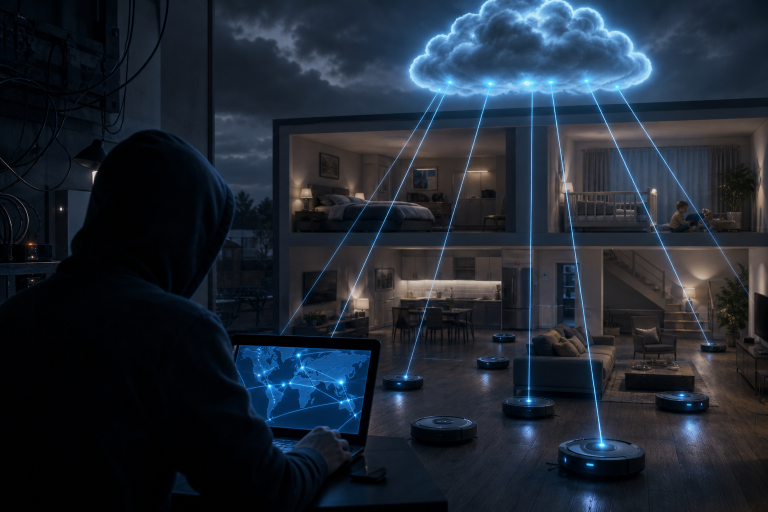
SharkNinja cloud flaw could let attackers remotely control millions of Shark robot vacuums
A security researcher found a critical flaw in SharkNinja's cloud-connected robot vacuum ecosystem that could allow remote code execution on affected devices. The issue affects millions of Shark robot vacuums, turning a consumer appliance…
Read the article →
Government, telecom, and public-sector breaches show persistent exposure of large identity datasets
The feed includes a series of large breaches affecting telecoms, insurers, government agencies, and public services, with millions of records exposed in some cases. These incidents often start with phishing, employee compromise, or third-party…
Read the article →
Microsoft’s July patch tsunami and the race to compress exploitation windows
Microsoft’s July 2026 Patch Tuesday was one of the biggest security releases in company history, with coverage across hundreds of vulnerabilities and multiple already exploited issues. Multiple outlets highlighted that the scale alone made…
Read the article →
Swiss banking and public-sector cyber agenda: NCSC, nLPD, and notification obligations keep gaining weight
Across the feed, the strongest Swiss-relevant signal is not a single breach but the steady hardening of governance expectations around cyber risk, privacy, and incident handling. The NCSC appears repeatedly in update-style items and…
Read the article →
The Russian cyber ecosystem faces escalating sanctions and enforcement actions
The U.S., UK, and EU widened sanctions and enforcement actions against Russian-linked cybercriminals, bulletproof hosting operators, and state-aligned actors. Officials said these networks were involved in ransomware enablement, cyber sabotage, and broader destabilization campaigns…
Read the article →
Lidl and EY both disclosed third-party support and service-provider data breaches
Lidl notified customers in Germany, Belgium, and the Netherlands that a breach at an external IT service provider exposed customer data stored in a separate file. The retailer said the incident did not affect…
Read the article →
CISA pushes vendors toward more disciplined coordinated vulnerability disclosure
CISA and allied agencies published new coordinated vulnerability disclosure guidance aimed at helping vendors handle reports more consistently. The guidance arrived shortly after CISA itself struggled to receive a serious report, which appears to…
Read the article →
ClickFix becomes a scalable social-engineering platform for malware delivery
ClickFix moved from a novelty to a widely used attack pattern that tricks users into running commands themselves, bypassing many endpoint defenses. Researchers said the technique now functions as an industrialized ecosystem, often using…
Read the article →