

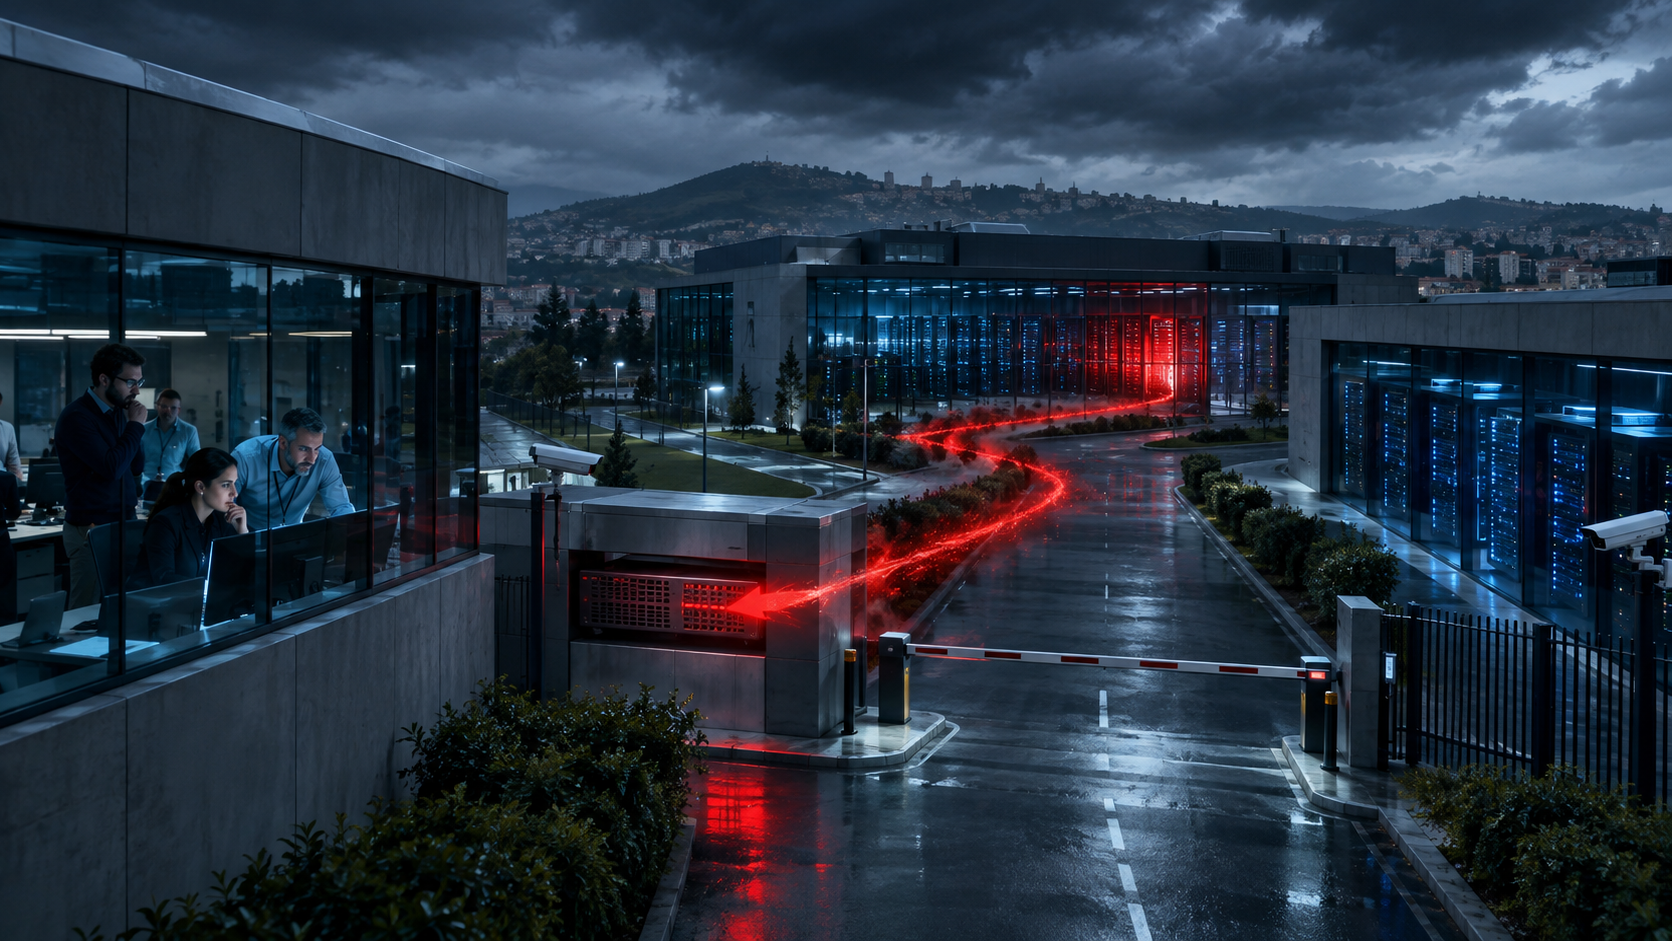
Attacks Chain Three Check Point Vulnerabilities and Reach VMware ESXi
Check Point researchers have documented attacks that began on October 30 against vulnerable Mobile Access gateways, including those at organizations in Israel and other countries. The attackers exploited the PHP2Shell vulnerabilities CVE-2026-109618 and CVE-2026-109619, then used CVE-2026-123039 to obtain root privileges, install backdoors, and move into VMware ESXi environments. In some incidents, destructive malware was deployed that erased data from servers, turning the intrusion into an operation with potentially irreversible consequences. CISA subsequently added CVE-2026-123039 to the Known Exploited Vulnerabilities catalog, confirming that the flaw has been exploited in real-world attacks. Attribution remains uncertain, and its inclusion in the KEV catalog makes mitigation a priority for affected organizations. Installing patches alone may not be sufficient: defenders must look for backdoors, compromised credentials, and signs of lateral movement that may already be present.
Source: /r/cybersecurity

Leave a Reply